OAuth2 and OIDC
So far, authentication in this course has meant a user typing a password into this application (see First app and Filter chain). That stops working once a system is made of several independent pieces: a browser-based frontend, a backend API, and perhaps a device that is not a browser at all, like a sensor on a bike. None of them should have to store or even see every user’s password, and a frontend running in a browser cannot keep a secret at all, since anyone can open its source.
OAuth2 solves this by introducing a fourth party whose only job is authentication: the Identity Provider (also called the Authorization Server). Everyone else trusts it instead of re-implementing login.
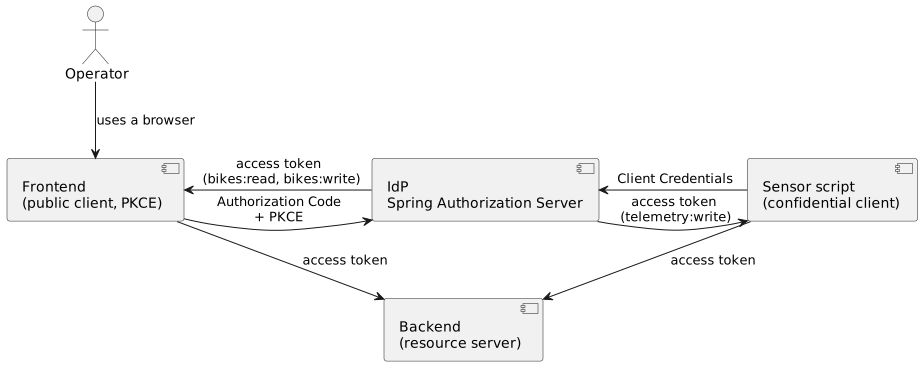
Four roles
-
The Resource Owner is whoever can grant access: our human operator.
-
The Client is the application requesting access on the Resource Owner’s behalf: our frontend. It can also be an application acting on its own behalf, with no human involved at all: our sensor script. Each client is registered with the Authorization Server in advance; see Run the IdP for how, and Log in from the frontend and Send sensor telemetry for each one in action.
-
The Authorization Server authenticates the Resource Owner (or the Client itself) and issues tokens: our IdP, detailed in Run the IdP.
-
The Resource Server holds the protected data and accepts or rejects tokens: our backend, detailed in Secure the backend.
Two grant types, for two different situations
A human operator is present, using a browser that can be redirected: the frontend uses the Authorization Code grant, hardened with PKCE (Proof Key for Code Exchange, pronounced "pixy") since a public, in-browser client cannot hold a client secret. The sensor script has no human and no browser, just a client ID and a secret it can keep to itself: it uses the Client Credentials grant instead.
Both ultimately produce the same kind of artifact: an access token.
The access token: a JWT
Our IdP issues access tokens as JWTs (JSON Web Tokens). A JWT is a signed, self-contained set of claims: who it was issued for, who issued it, when it expires, and which scopes it was granted. Because it is signed, the backend can verify it using the IdP’s public key alone, without calling the IdP back on every request. We will decode a real one by hand in the next section.
A scope is not "who are you", it is "what was this particular token authorized to do".
The frontend’s token will carry bikes:read and bikes:write; the sensor’s token will carry only telemetry:write.
The backend will enforce these scopes independently of which client happened to present the token, which is exactly the distinction a plain "authenticated or not" check cannot make.
Standards, not just this one server
Jakarta Persistence had a specification with several providers (Hibernate, EclipseLink). OAuth2 and OpenID Connect (OIDC, which layers standardized identity on top of OAuth2) work the same way: they are specifications, not a single product. Keycloak and Authentik are two popular, full-featured Identity Providers you are likely to meet professionally. We use a much smaller one, Spring Authorization Server, precisely because its configuration fits in a page of YAML, but the grant types, scopes, and JWTs it produces are the same ones those larger servers produce.
Hands-on, in four steps
Clone the exercise once, then run each piece in its own terminal, in this order:
$ git clone https://gitlab.com/noseda_a/bikeshare-security.git
-
Run the IdP and inspect the two clients it registers.
-
Secure the backend with scope-based authorization.
-
Log in from the frontend with Authorization Code + PKCE.
-
Send sensor telemetry with Client Credentials.
Budget 60 to 90 minutes for all four.